TechCrypto address “copy and paste attack” persists after Sality botnet disruption
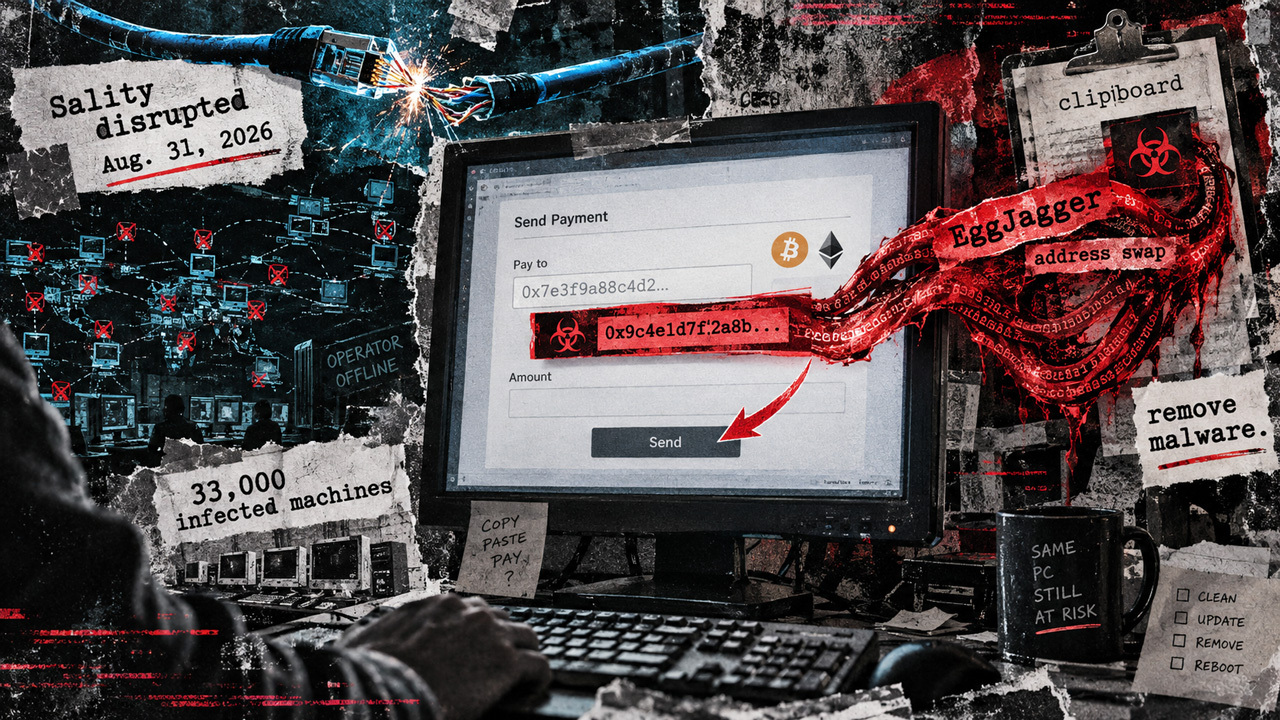
The Aug. 31 operation against the Sality botnet stopped its operator from delivering new malware, but threats already installed on infected computers remain active. CrowdStrike said EggJagger monitors the clipboard and replaces copied Bitcoin or Ethereum addresses with attacker-controlled ones, so infected devices still require malware removal.
C CryptoSlate★★☆☆☆2026-09-08 14:35Original
Crypto address “copy and paste attack” persists after Sality botnet disruption
 Tech